Cronzy Watch capability
Fix the vulnerabilities attackers actually use
A scanner can give you ten thousand findings sorted by severity. Cronzy Watch sorts them by what is being exploited, on which asset, and whether anything is known to fix it, so your team starts with the short list that matters.
What you get
Vulnerability prioritisation, in practice
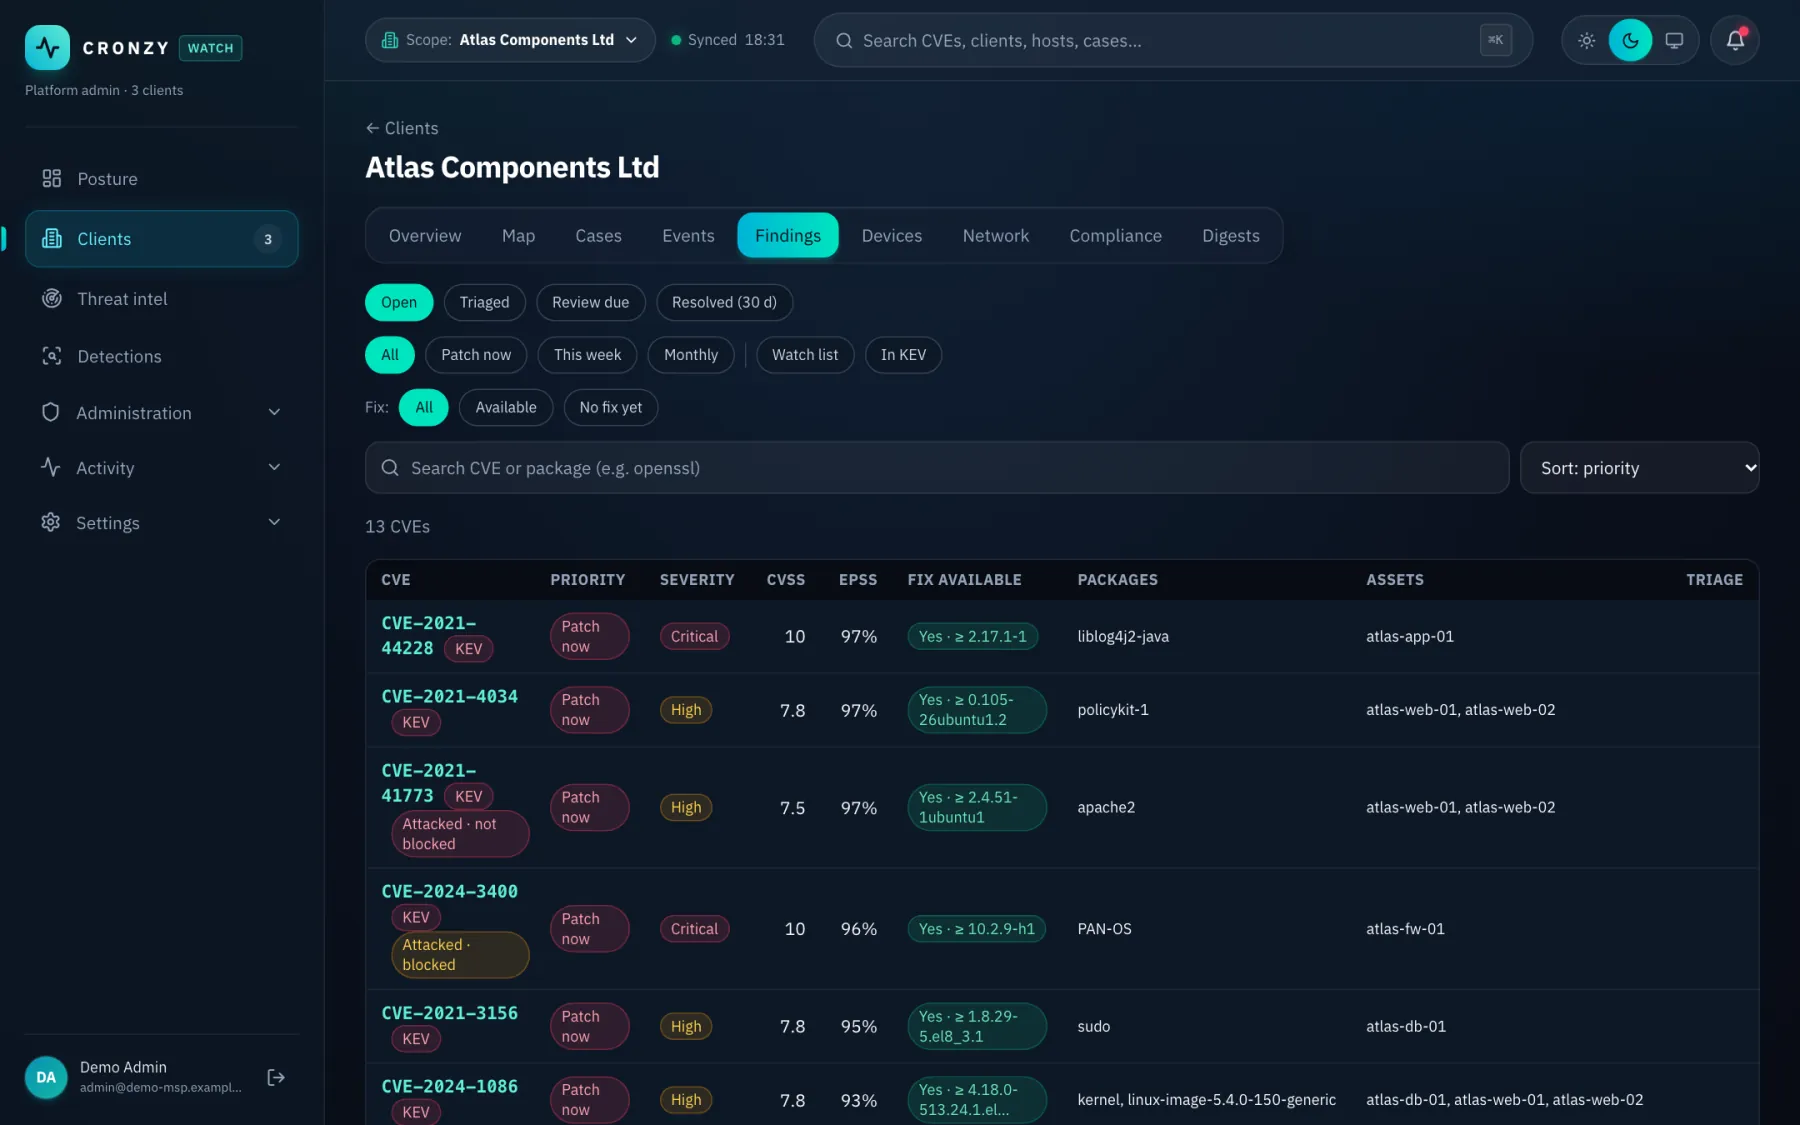
Known exploited first
Vulnerabilities in the CISA Known Exploited Vulnerabilities catalog (KEV) are marked and ranked above the rest, because there is evidence that attackers use them.
Likelihood, not only severity
EPSS, the exploit prediction score, adds how likely a CVE is to be exploited soon. A CVSS 9.8 nobody exploits no longer outranks a CVSS 7.5 that is under attack.
Your own evidence
When the firewall logged exploit attempts that were not blocked, the matching CVE moves up and the affected assets are named.
Fix availability on the line
Each CVE shows whether a vendor fix exists. CVEs with no vendor fix get their own line and are capped per asset, so they do not drown the list.
Risk per asset and per client
Findings roll up into a risk score per asset, weighed by criticality and exposure, and into a view across all your clients.
How it works
From connected to done
- Cronzy reads vulnerabilities and agents from Wazuh, AWS Inspector and the other connected sources.
- Each CVE is matched against CISA KEV and EPSS, and against what your firewall has seen.
- The result is a ranked list with the affected assets, the fix status and a deadline.
- Open any CVE to get its remediation plan, and mark it fixed when done.
Questions
Frequently asked questions
Why not just sort by CVSS?
CVSS describes how severe a flaw is in theory. It does not say whether anyone exploits it. KEV and EPSS add that, which is why the order changes.
Where does the KEV and EPSS data come from?
KEV is published by the US Cybersecurity and Infrastructure Security Agency (CISA). EPSS is published by FIRST. Both are public data.
Does it replace my vulnerability scanner?
No. Cronzy reads the findings your sources already produce (for example Wazuh and AWS Inspector) and ranks and explains them.
Terms used on this page
Keep reading
Related capabilities
How to fix: remediation plans
A plan per CVE and the exact firewall commands for attacks, ready to paste.
Attack correlation and cases
Scattered alerts become one case with severity, deadline and a timeline.
Compliance view (CIS, ISO 27001)
Your evidence mapped to CIS Controls v8 and ISO 27001 Annex A. A view, not a certification.
See it on a demo estate
Tell us about your environment and we will show Cronzy Watch with data that matches it.