Cronzy Watch capability
A network map you did not have to draw
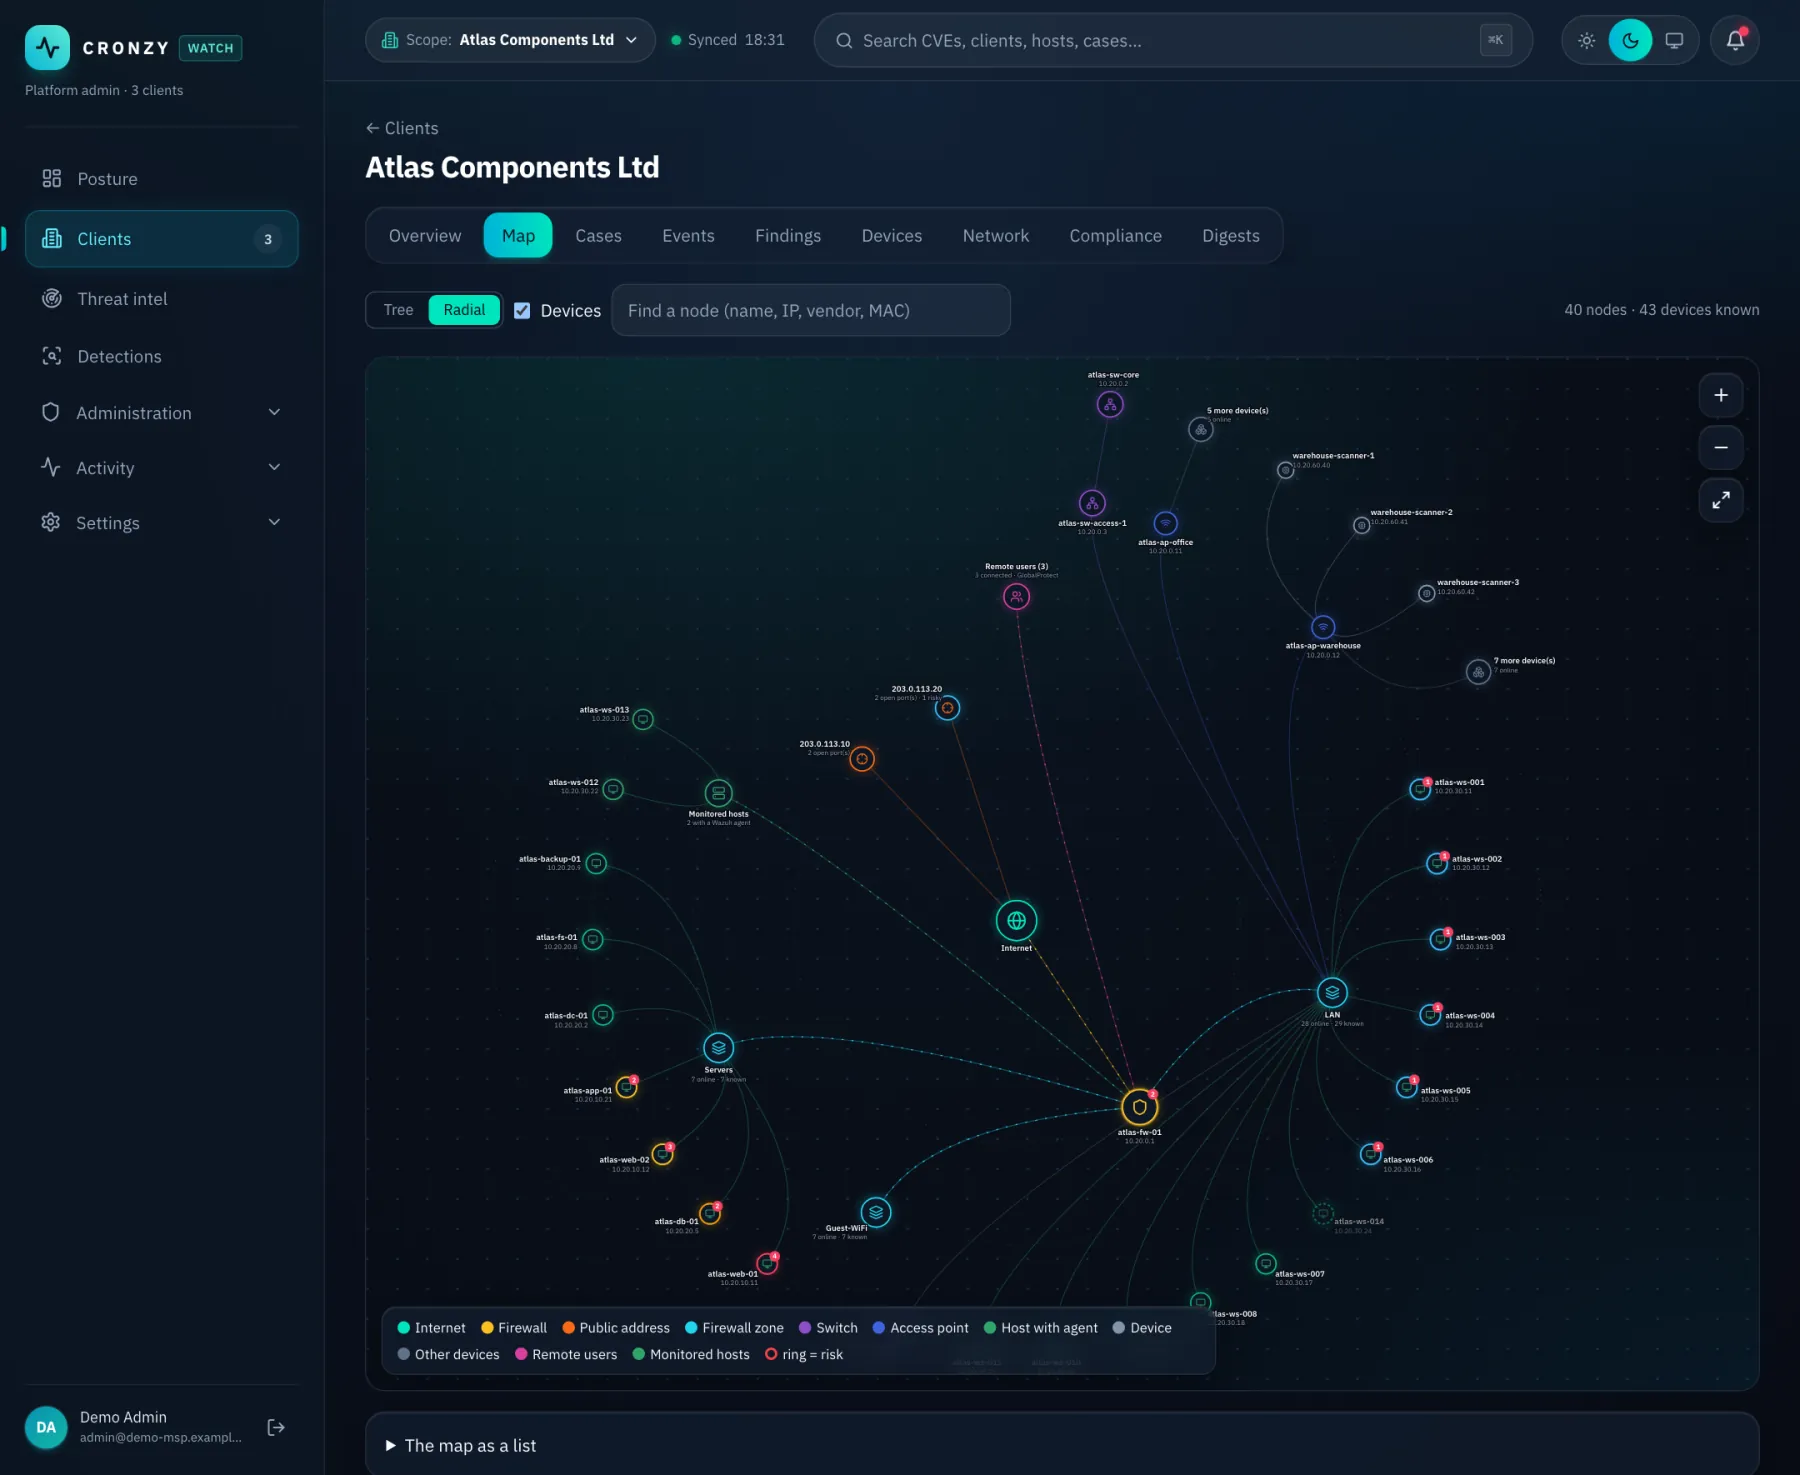
Cronzy Watch builds the map from the systems that already know the network, and colours each node by risk, so a glance shows where to look first.
What you get
Network map, in practice
Built from real sources
Firewall zones, Cisco and UniFi switches, access points, servers and Wi-Fi clients, merged into one picture.
One device, one entry
The same device seen by several sources is merged by its hardware address, so you do not get duplicates.
Coloured by risk
Each node carries the risk of its findings and cases. Click one to see why.
What the Internet sees
Exposure checks show which services are reachable from outside.
How it works
From connected to done
- Connect the firewall and the switches. Cronzy reads inventory and neighbours.
- Agents and cloud sources add the hosts behind them.
- The map is drawn per client and updates as the sources sync.
Questions
Frequently asked questions
Which switches are supported?
Cisco switches over SNMPv3 and UniFi switches are supported for inventory and the map.
Can I name devices myself?
Yes. People can give devices a name, and it is kept.
Keep reading
Related capabilities
Palo Alto firewall security
Configuration checks, advisories, GlobalProtect and threat logs, turned into cases.
Internet exposure and discovery
What the Internet sees, and assets nobody told you about.
Vulnerability prioritisation
The list starts with what attackers actually use: CISA KEV and EPSS, not CVSS alone.
See it on a demo estate
Tell us about your environment and we will show Cronzy Watch with data that matches it.