For MSPs
See every client’s risk in one place, and keep each client apart
Managed service providers need one dashboard for the whole book and a hard wall between clients. Cronzy Watch is built that way: ranked risk across all clients on the front page, and each client’s data strictly separate underneath.
What you get
Cronzy Watch for MSPs, in practice
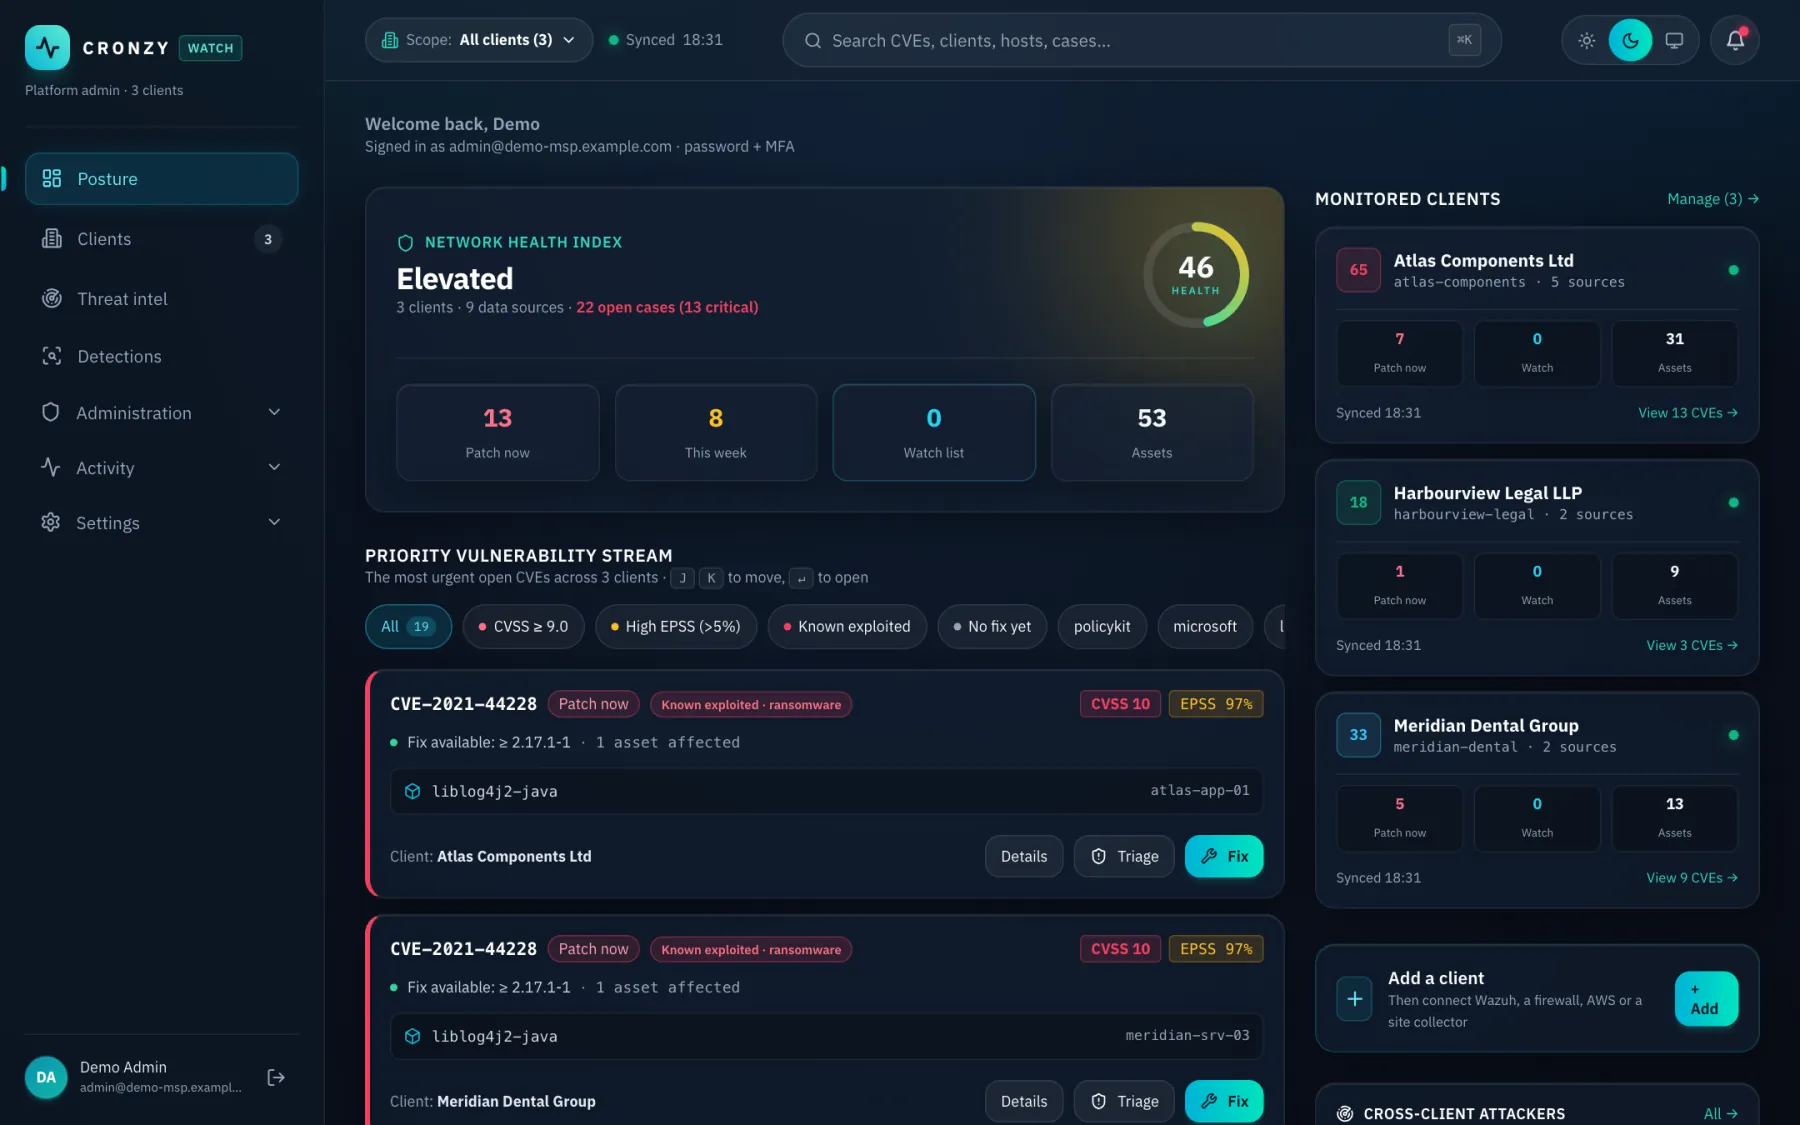
One view, every client
The dashboard shows each client with its risk score and the most urgent items, so you start the day with who needs attention.
Strict separation
Row-level security in the database keeps one client’s data from another’s, even if application code has a bug. Roles decide who can see which clients.
Roles, MFA and single sign-on
Platform administrators, client administrators and custom roles, with multi-factor authentication and single sign-on, and an audit trail of what people did.
Work ranked across the book
The same ranking by real exploitation applies to every client, so the whole team works from the same priorities.
A compliance view per client
CIS Controls v8 and ISO 27001 Annex A mapped to each client’s evidence, for review conversations.
Response with a second approver
Blocking an address or isolating a host needs a different person to approve it, which suits teams with shared duties.
How it works
From connected to done
- Add a client and connect its sources: Wazuh, firewalls, AWS, Cisco and UniFi, directly or through a site collector.
- Cronzy ranks the client’s vulnerabilities and opens cases for attacks.
- Your team works the queue across clients, with deadlines and e-mail on critical cases.
- Use the compliance view and the case history when you talk to the client.
Questions
Frequently asked questions
How are clients kept separate?
With row-level security in the database, plus roles. A query made for one client cannot return another client’s rows.
Can one person see all clients?
Platform administrators can. Client administrators and custom roles are limited to the clients they are given.
Do I need to install anything at the client?
Not always. Cloud sources connect directly. For sites that cannot be reached from the Internet there is an optional outbound-only site collector.
Terms used on this page
Keep reading
Related capabilities
Vulnerability prioritisation
The list starts with what attackers actually use: CISA KEV and EPSS, not CVSS alone.
Compliance view (CIS, ISO 27001)
Your evidence mapped to CIS Controls v8 and ISO 27001 Annex A. A view, not a certification.
Response with four-eyes approval
Block an address or isolate a host. One person requests, another approves, all audited.
See it on a demo estate
Tell us about your environment and we will show Cronzy Watch with data that matches it.